The Radar post-quantum TLS support checker now also reports TLS bugs detected during the handshake test. When a scanned host exhibits compatibility issues, the results include details on the specific bugs detected, along with guidance on how to investigate and remediate each issue. The bugs section only appears for hosts where issues are found.
The following TLS bugs are detected:
- Split ClientHello — The connection fails with a fragmented post-quantum
ClientHellobut succeeds with classical handshakes. Typically caused by middleboxes or firewalls that cannot reassemble split TLS messages. - HRR Failure — The server sends a
HelloRetryRequestbut fails to complete the handshake afterward. - Unknown Keyshare — The server cannot handle unknown key exchange algorithms and fails instead of responding with a
HelloRetryRequestas required by the TLS 1.3 specification.
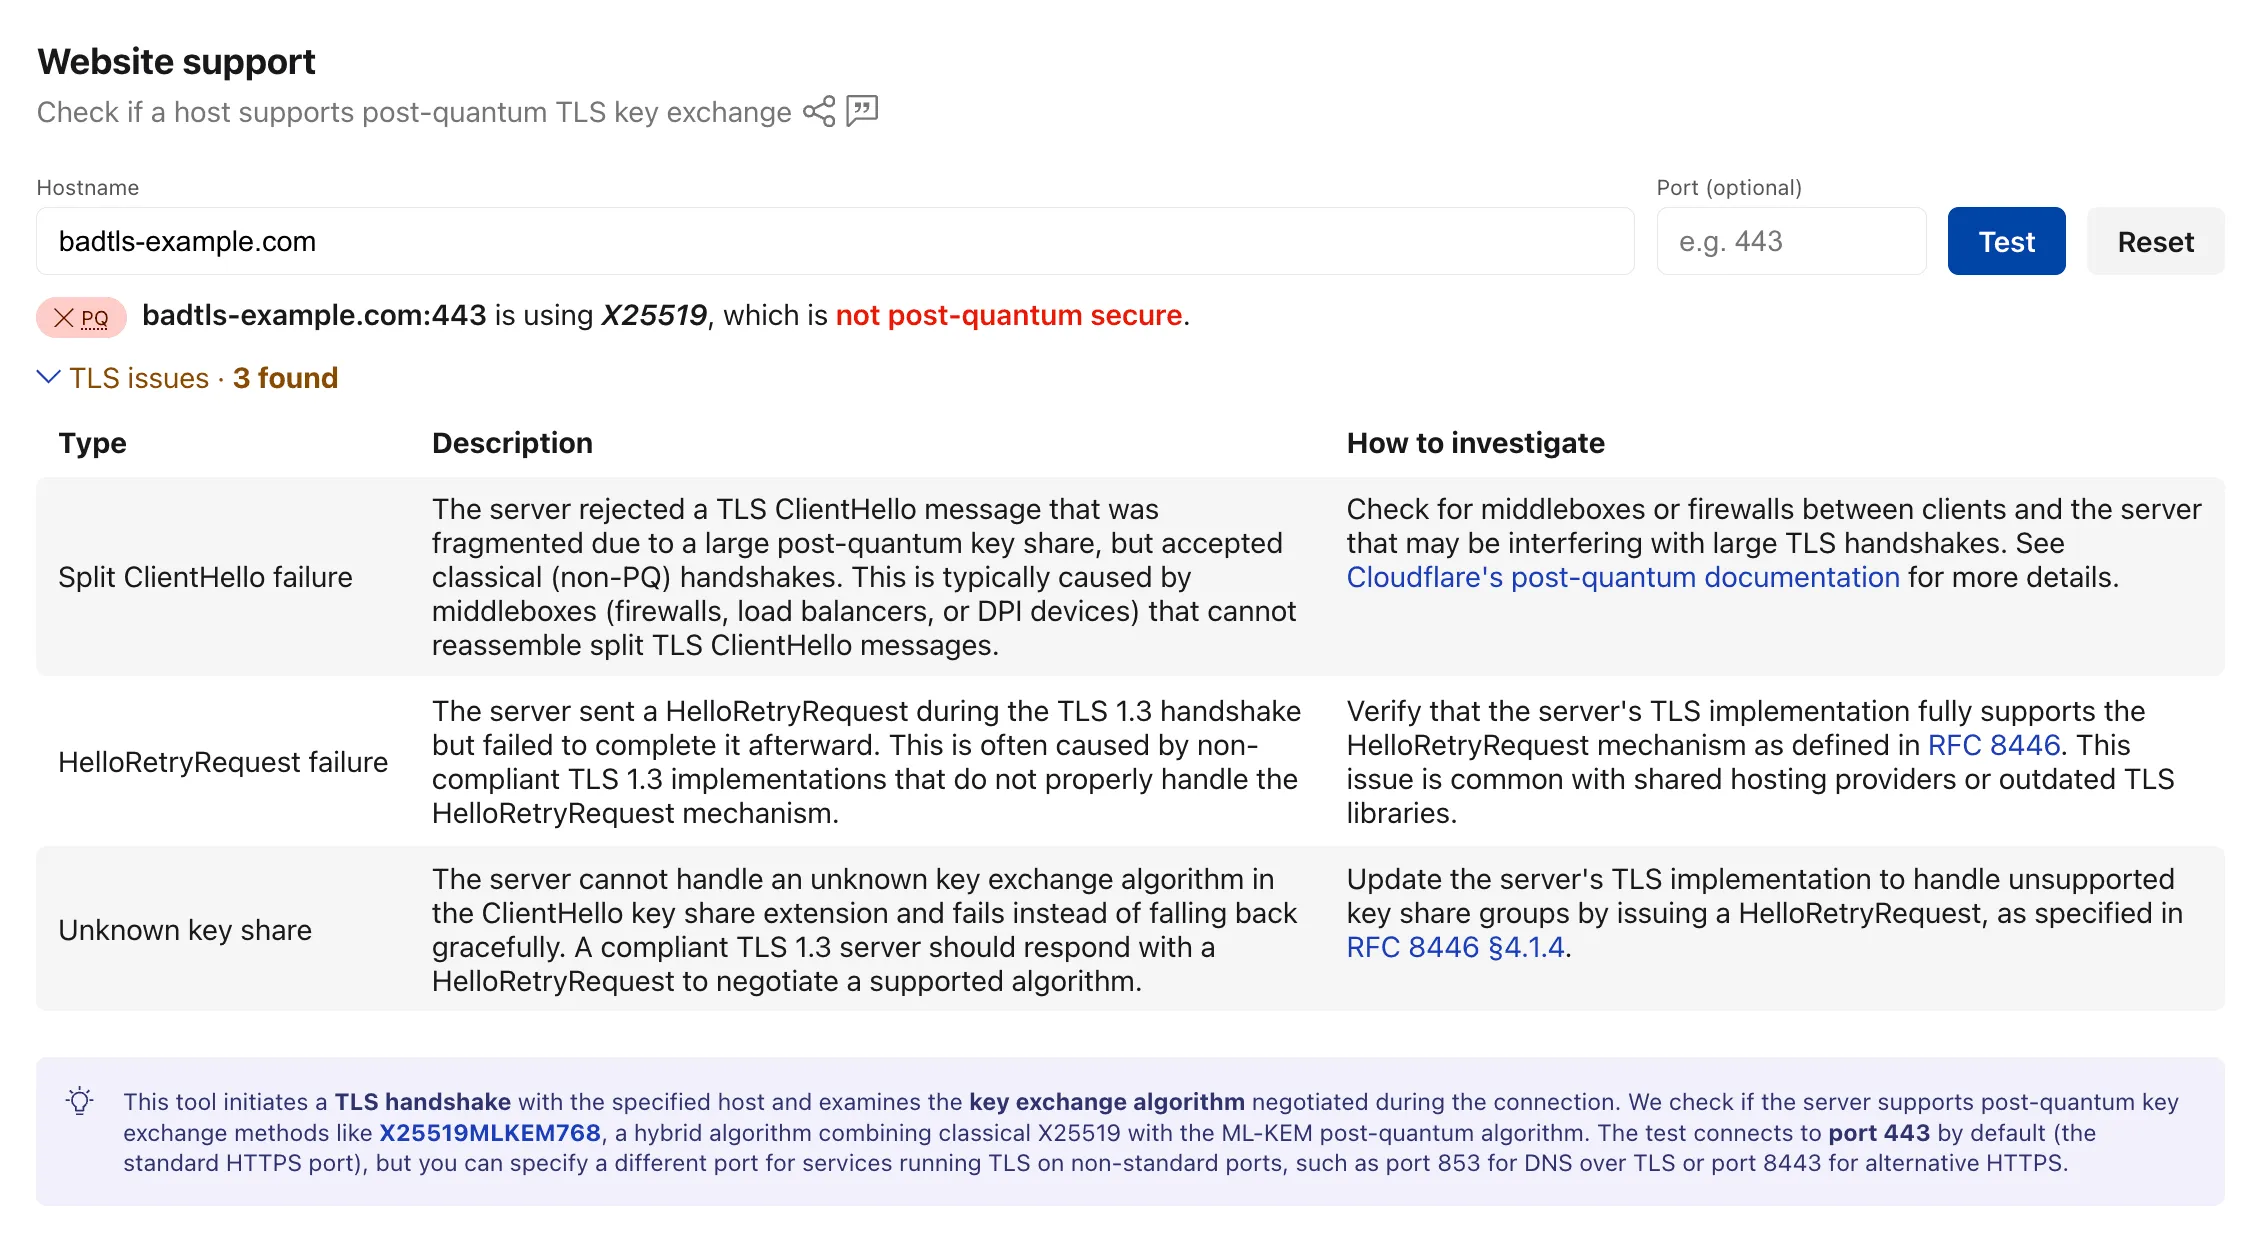
Bug detection data is available through the existing /post_quantum/tls/support endpoint.
Visit the Post-Quantum Encryption page to test a host.
Source: Cloudflare
Latest Posts
- MC1450134: Microsoft Entra Recognizes Windows Hello for Business and macOS Platform SSO as Standalone MFA Factors

- MC1506982: Microsoft 365 Apps Gets October 2026 Updates for All Channels
- AWS Agent Registry now supports custom metadata for registry records
- Amazon Location Service launches an interactive API Playground featuring Places, Routes and Maps APIs