Take a look and decide whether this affects your tenant, users or support teams.
Primary Audience
Why this score?
AT A GLANCE
END USERS
IT ADMINS
ROLLOUT TIMELINE
Late November 2026
📢 Official Microsoft Message Center Announcement
Microsoft SharePoint: Data access governance report for group permissions
Message ID: MC1540348
[What and why]
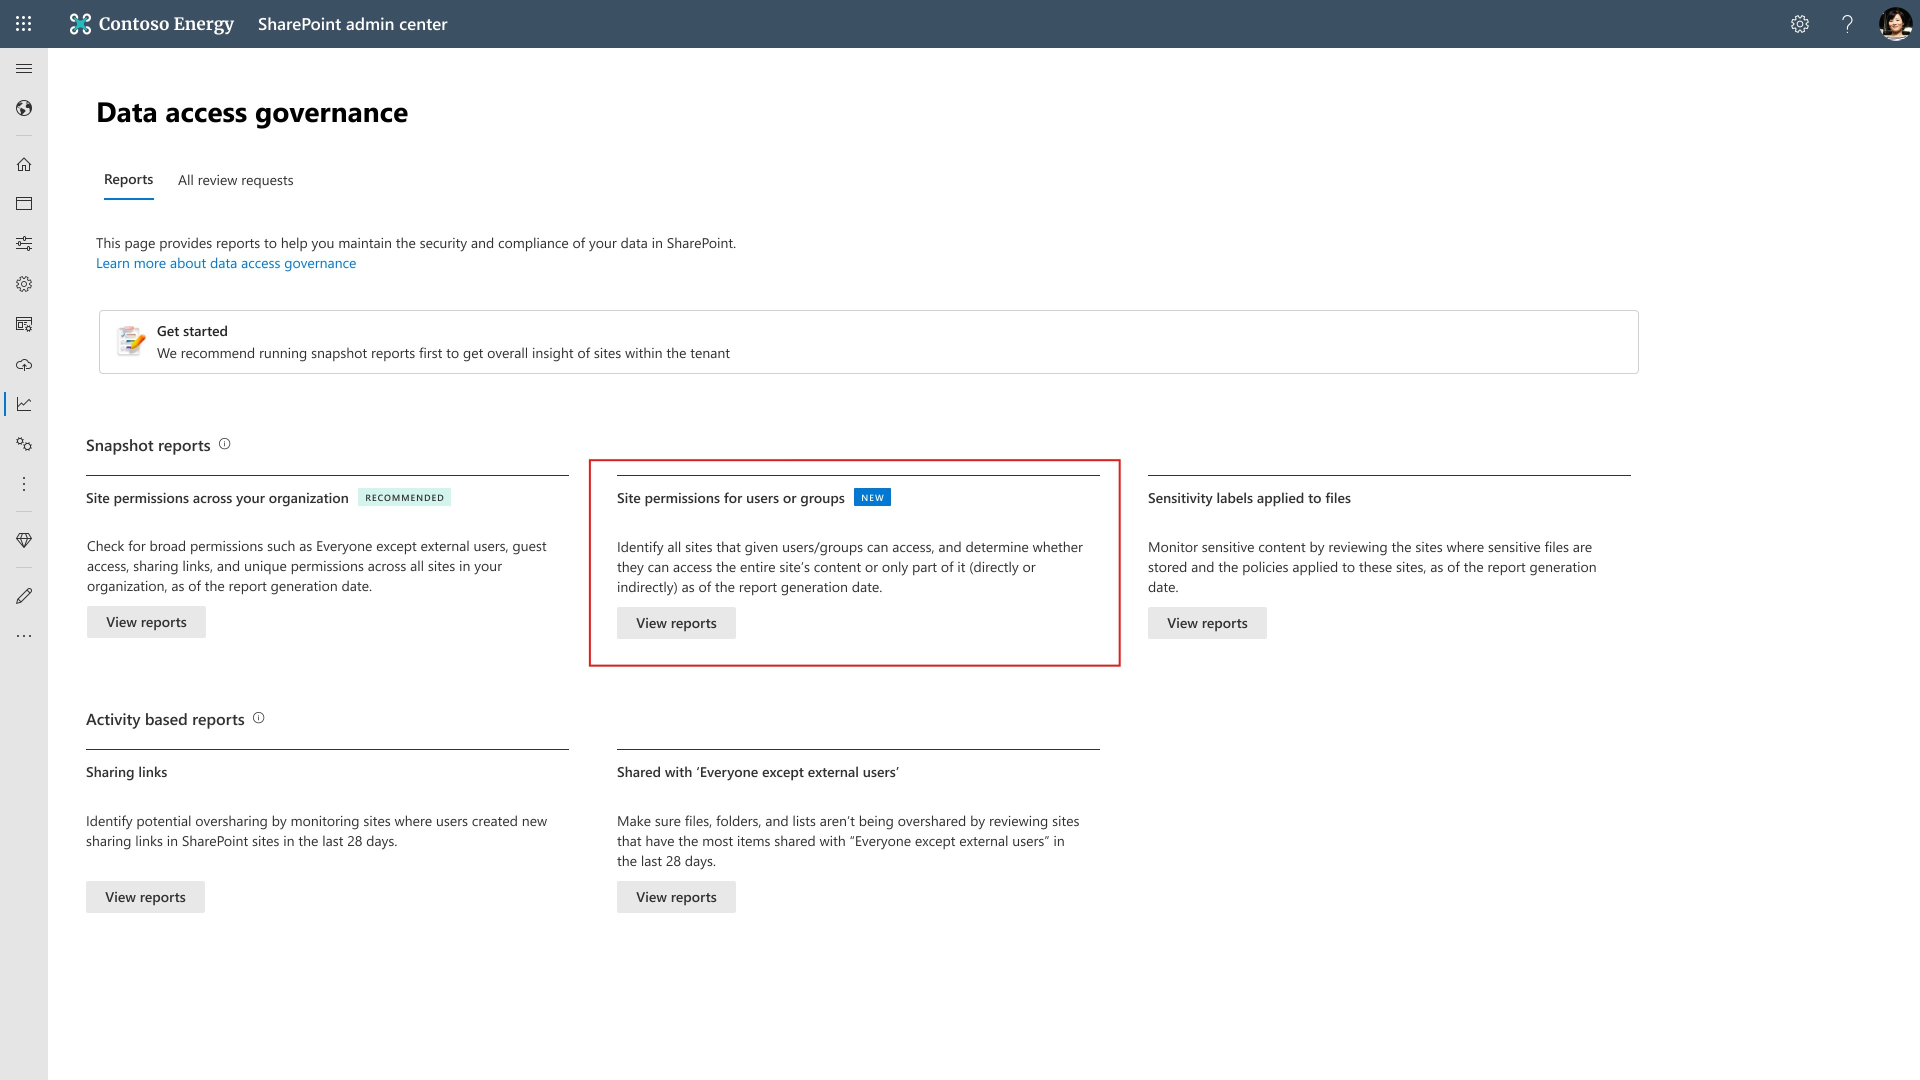
We are introducing a new Data access governance report in the SharePoint admin center that allows SharePoint administrators to identify all sites accessible to a given group and the extent of that access. Groups with broad membership, including groups created for vendors, can expose sensitive content to unintended recipients. This report helps administrators investigate potential exposure and verify group permissions.
[Rollout schedule]
- General Availability (Worldwide, GCC, GCC High, DoD): Rollout will begin in late November 2026 and is expected to complete by early December 2026.
[Impact on your organization]
Who is affected
- SharePoint administrators responsible for managing and reviewing site permissions.
Platforms and services
- Microsoft SharePoint admin center
- Data access governance
What will happen
- SharePoint administrators will be able to use the new report to identify all sites accessible to a given group. The report will show the extent of the group’s access to those sites.
- Administrators can use the report to investigate potential exposure of sensitive content and to review group permissions before assigning Copilot licenses.
Data access governance page
[Action required and recommendations]
We recommend that you:
- Review your current SharePoint site permissions configuration to identify potential exposure.
- Notify your SharePoint administrators about the new reporting capability in the SharePoint admin center.
- Update your internal documentation and workflows to reflect this change.
[Learn more]
[Compliance considerations]
No compliance considerations identified. Review as appropriate for your organization.
Source: Microsoft Message Center • Analysed by MWPro