Take a look and decide whether this affects your tenant, users or support teams.
Primary Audience
Why this score?
AT A GLANCE
END USERS
IT ADMINS
ROLLOUT TIMELINE
Early December 2026
📢 Official Microsoft Message Center Announcement
Microsoft Defender: Similar cases comes to the unified security operations platform
Message ID: MC1556107
[What and why]
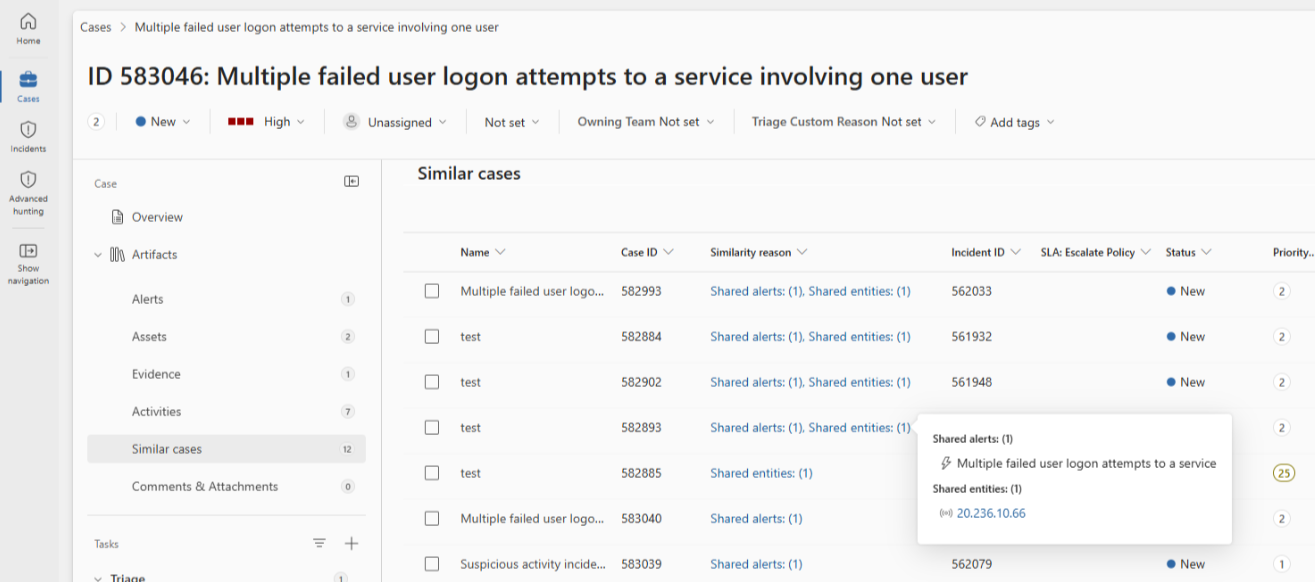
A new Similar cases tab appears on the incident page in the Microsoft Defender portal. The tab lists up to 20 incidents that share alert titles or entities with the current incident, helping security analysts identify recurring patterns and see how similar cases were handled. The Similarity reason column shows why each incident appears in the list.
This update brings the Similar incidents experience from Microsoft Sentinel in the Azure portal to the unified security operations platform. As part of this update, the Associated incidents card on the Summary tab will be renamed Recommended correlations. Similar cases show separate cases that share alert titles or entities, while Recommended correlations identifies cases that are likely part of the same attack. The content of the renamed card will not change.
[Rollout schedule]
- Public Preview: Available now.
- General Availability (Worldwide): We will begin and complete rollout in early December 2026.
[Impact on your organization]
Who is affected
- Security analysts who investigate cases in the Microsoft Defender portal, including Microsoft Sentinel customers who use the Defender portal
Platforms and services
- Microsoft Defender portal
- Microsoft Defender XDR
- Microsoft Sentinel in the Defender portal
What will happen
- A new Similar cases tab will appear on the case page:
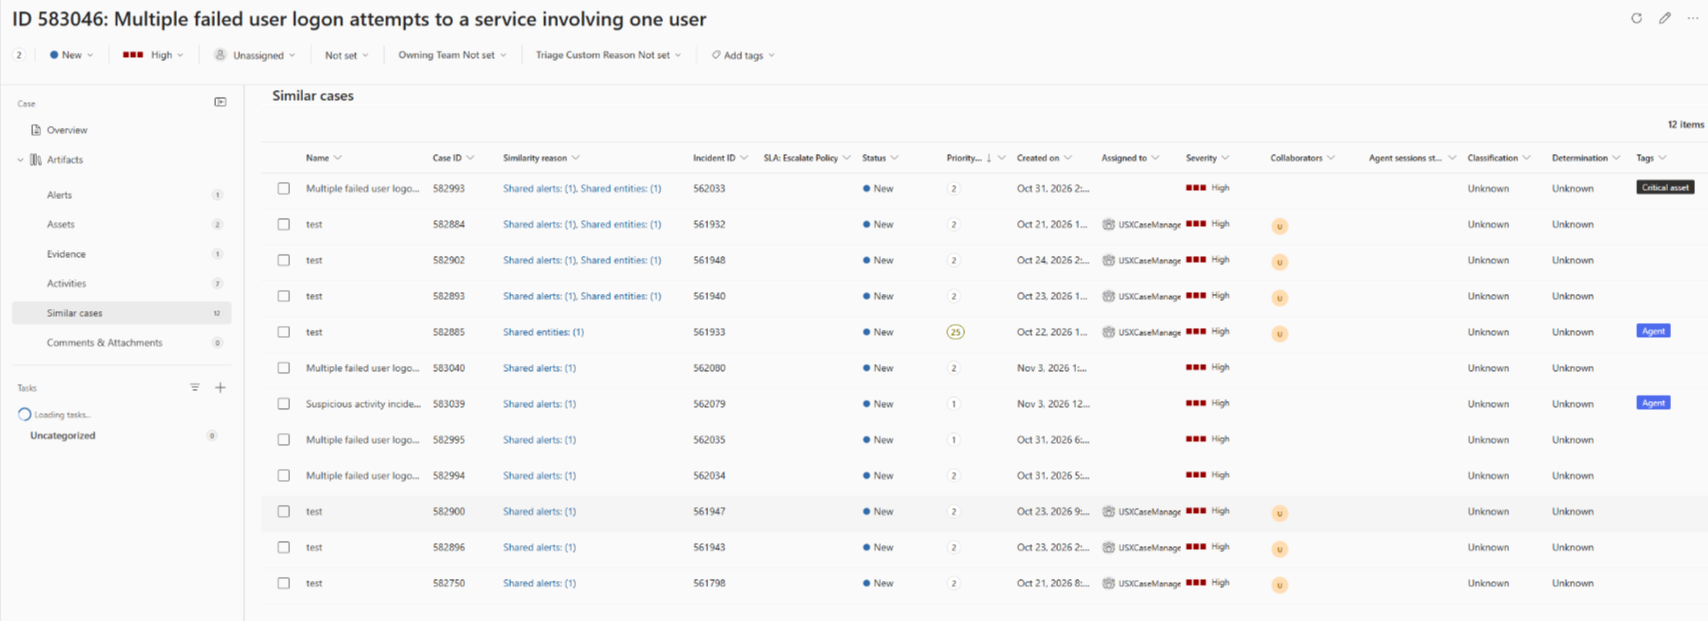
- The tab will list up to 20 cases that share alert titles or entities with the current incident.
- The Similarity reason column will show why an incident appears in the list. Analysts can hover over the info icon to view the items the cases have in common:
- The Associated incidents card on the incident Summary tab will be renamed Recommended correlations.
- The content of the renamed card will not change.
[Action required and recommendations]
No action is required to prepare for this change.
Learn more
- Alert correlation and incident merging in the Microsoft Defender portal – Microsoft Defender XDR | Microsoft Learn
- Investigate incident cases in the Microsoft Defender portal – Microsoft Defender XDR | Microsoft Learn
- Investigate incidents in the Microsoft Defender portal (Legacy) – Microsoft Defender XDR | Microsoft Learn
[Compliance considerations]
No compliance considerations identified. Review as appropriate for your organization.
Source: Microsoft Message Center • Analysed by MWPro