Cloudflare Access for private hostname applications can now secure traffic on all ports and protocols.
Previously, applying Zero Trust policies to private applications required the application to use HTTPS on port 443 and support Server Name Indicator (SNI).
This update removes that limitation. As long as the application is reachable via a Cloudflare off-ramp, you can now enforce your critical security controls — like single sign-on (SSO), MFA, device posture, and variable session lengths — to any private application. This allows you to extend Zero Trust security to services like SSH, RDP, internal databases, and other non-HTTPS applications.
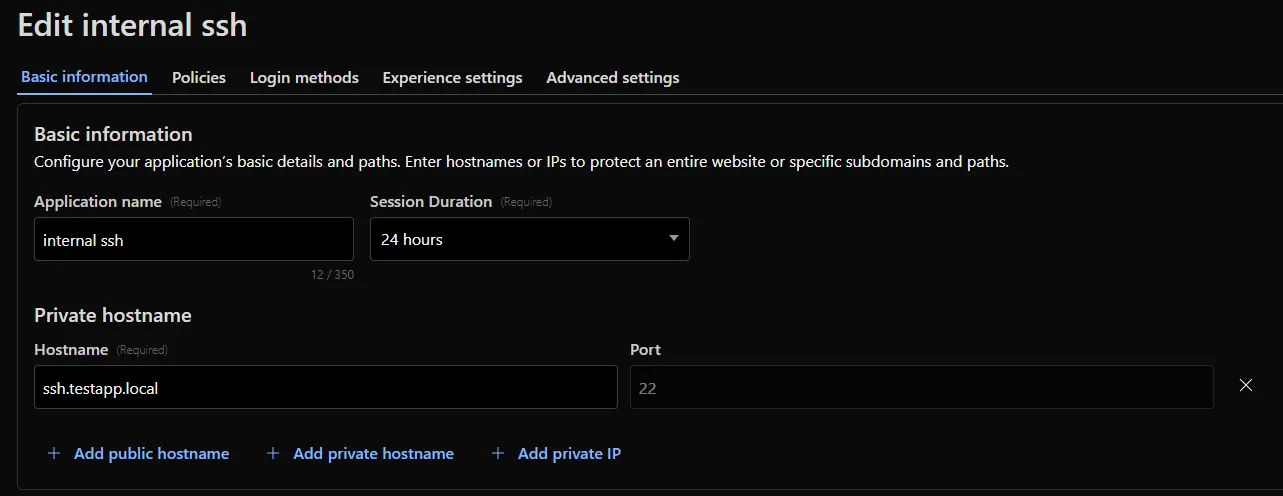
For example, you can now create a self-hosted application in Access for ssh.testapp.local running on port 22. You can then build a policy that only allows engineers in your organization to connect after they pass an SSO/MFA check and are using a corporate device.
This feature is generally available across all plans.
Source: Cloudflare
Latest Posts
- MC1471573: Copilot Studio Adds Support for MCP-Compliant Tools in Agent Workflows

- Microsoft 365 Weekly Change Intelligence – 1 Critical & 16 High Impact Changes (13 September 2026)
- AWS Elemental MediaLive enables frame-accurate pipeline locking for streams without timecode
- MC1470901: Microsoft Teams Adds Rule Duplication, Bulk User Upload, and Delete Options to Real-Time Alerting Management